the iso 27001 isms template for notion
Implement ISO 27001:2022 without starting from scratch.
A complete Information Security Management System in Notion.
Pre-built, cross-linked and sized for small, cloud-first businesses.
My Experience. My Guides. My Templates.
It is the structure I use with my own consulting clients, now packaged so you can run the project yourself, with plain-English guidance and a short video at every step.

£295, one-off payment. Instant delivery as a Notion duplicate link. Licensed for a single organisation.
What’s inside
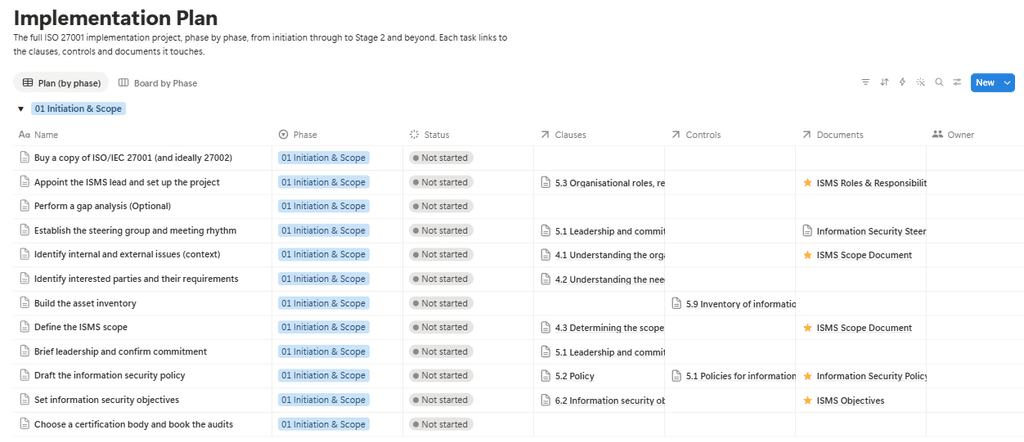
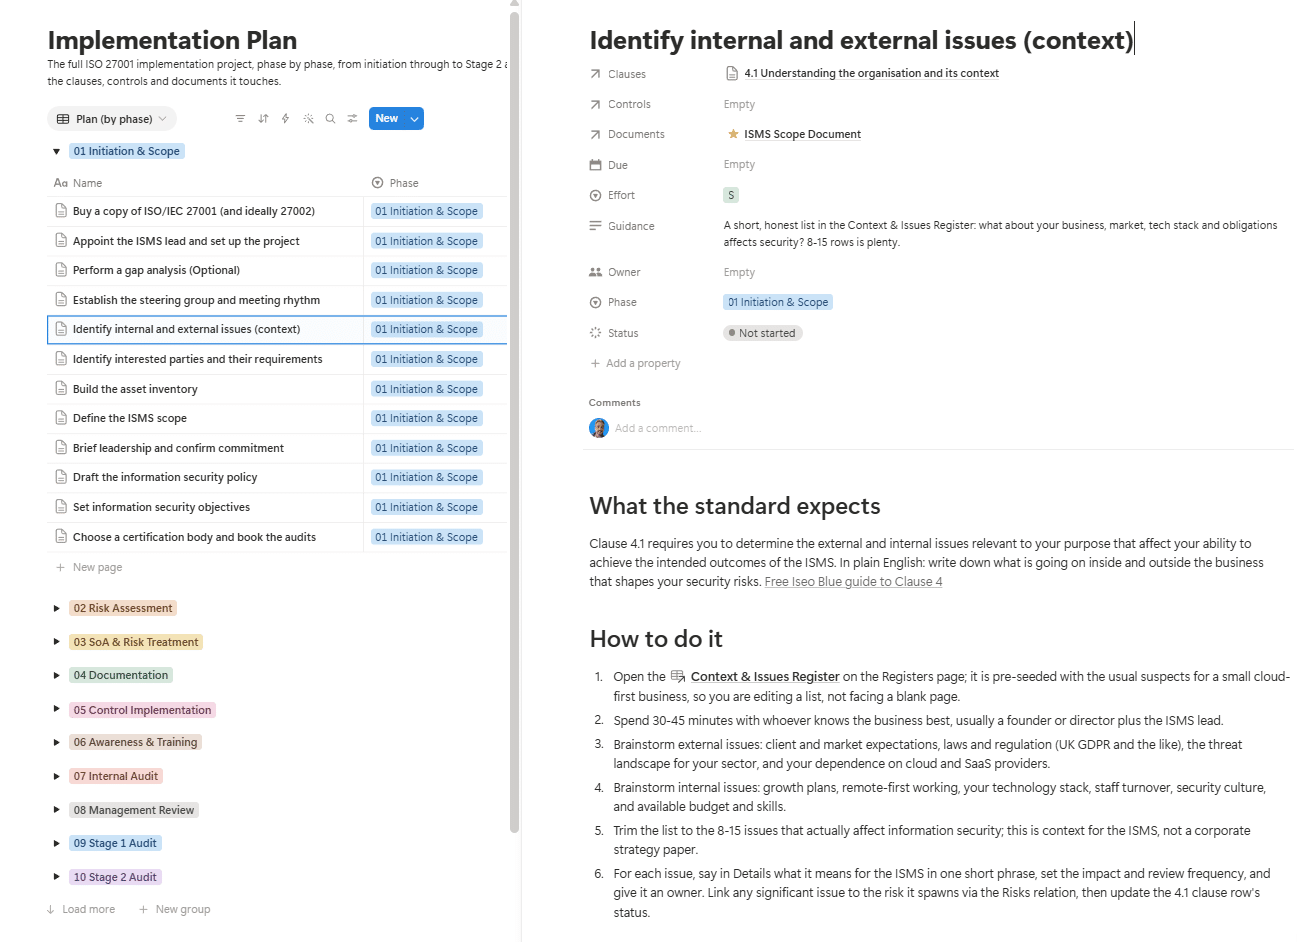
The Implementation Plan
A step-by-step recipe for delivery.
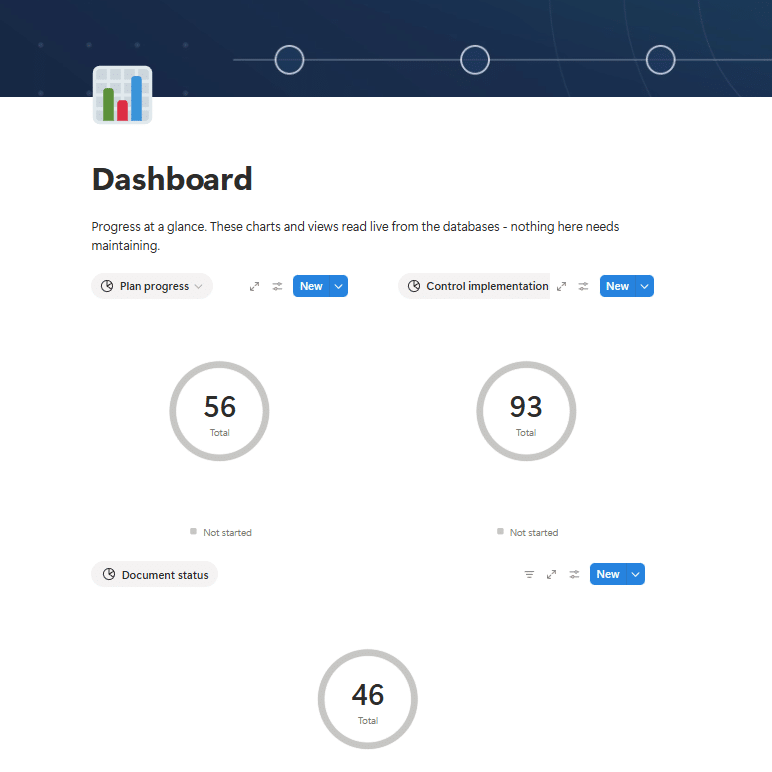
56 tasks across 11 phases, from initiation through Stage 1 and Stage 2 to life after certification.
Every task links to the clauses, controls and documents it touches, and opens into plain-English guidance: what the standard expects, how to do it, and roughly how long it takes.
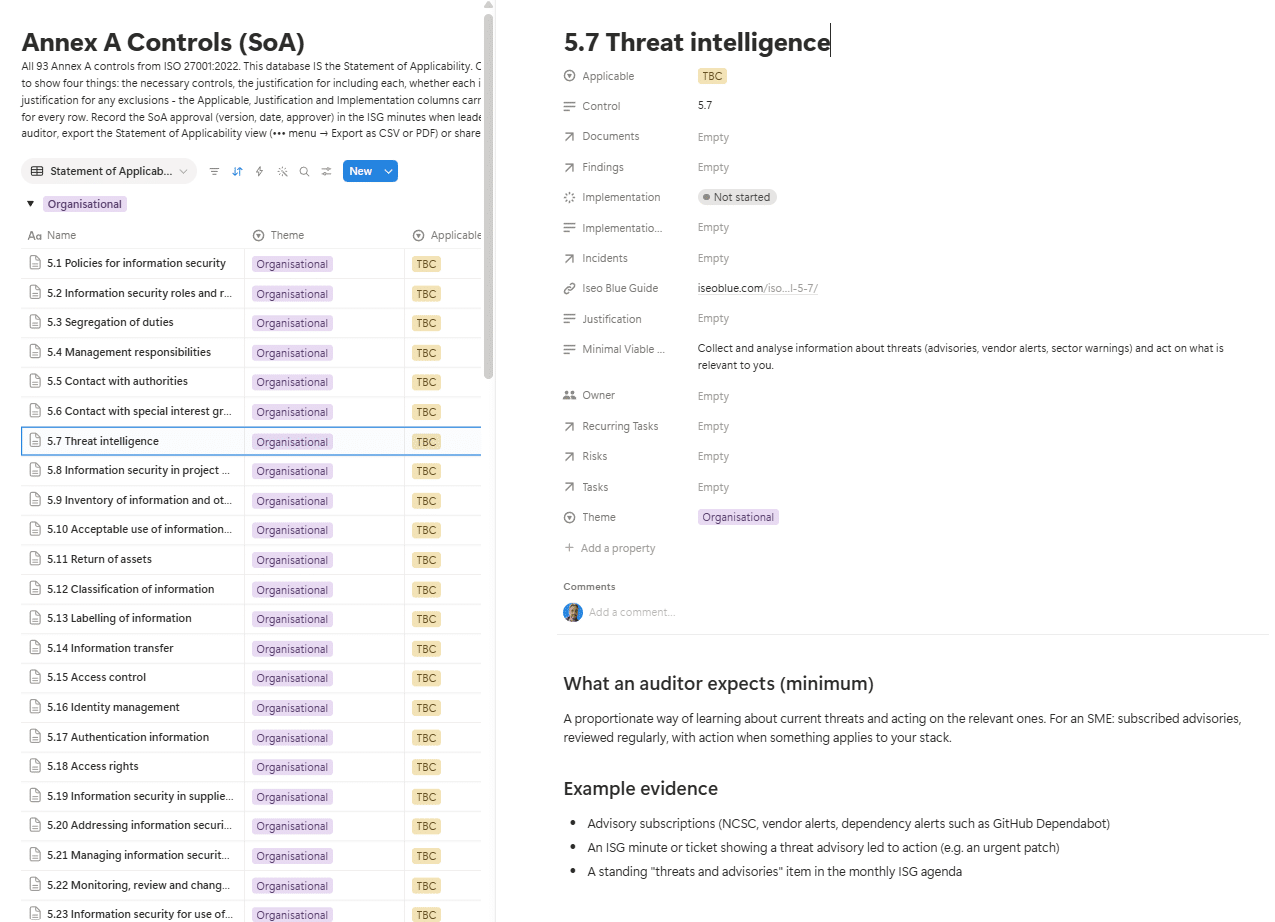
The Statement of Applicability
All 93 Annex A controls in one database.
Each control sets out what an auditor expects as a minimum for a small business, with example evidence.
The Document Library
46 pre-drafted policies, procedures and supporting documents.
Ready for you to adapt to your business.
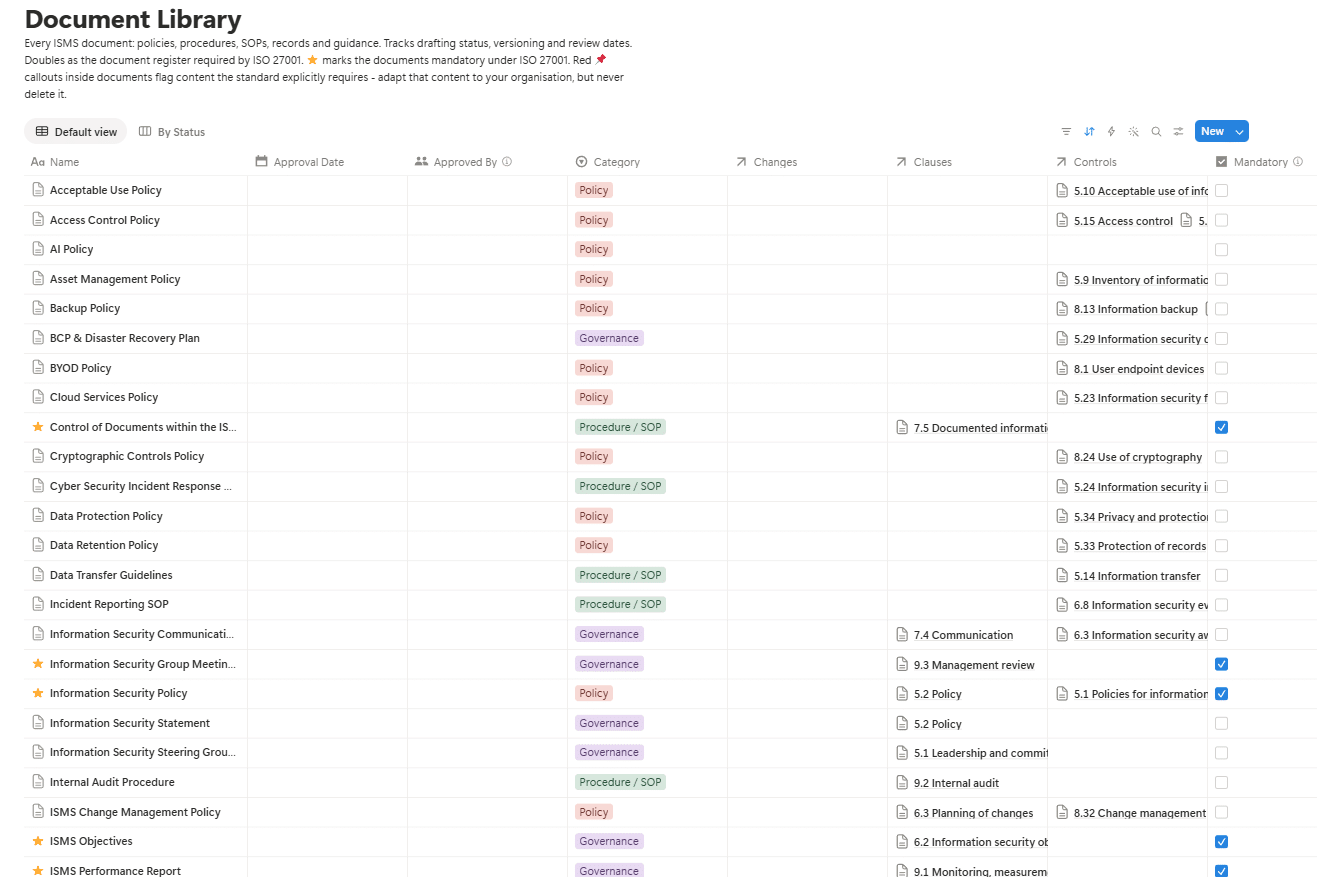
Every document arrives pre-drafted and cross-linked to the controls and clauses it satisfies. The ten documents ISO 27001 explicitly requires are marked ★.
| Ref | Document | Mandatory |
|---|---|---|
| Policies (21) | ||
| P1 | Information Security Policy | ★ |
| P2 | Acceptable Use Policy | |
| P3 | Access Control Policy | |
| P4 | BYOD Policy | |
| P5 | Data Protection Policy | |
| P6 | Data Retention Policy | |
| P7 | Mobile Device Policy | |
| P8 | Password Policy | |
| P9 | Patching & Vulnerability Management Policy | |
| P10 | Secure Development Policy | |
| P11 | Supplier Security Policy | |
| P12 | Asset Management Policy | |
| P13 | Cloud Services Policy | |
| P14 | Remote Working Policy | |
| P15 | ISMS Change Management Policy | |
| P16 | Physical Security Policy | |
| P17 | AI Policy | |
| P18 | Malware Policy | |
| P19 | Backup Policy | |
| P20 | Cryptographic Controls Policy | |
| P21 | Logging & Monitoring Policy | |
| Governance (12) | ||
|---|---|---|
| G1 | ISMS Scope Document | ★ |
| G2 | ISMS Objectives | ★ |
| G3 | Information Security Statement | |
| G4 | ISMS Roles & Responsibilities | ★ |
| G5 | Metrics & Reporting Approach | |
| G6 | BCP & Disaster Recovery Plan | |
| G7 | Special Interest Groups & Forums | |
| C1 | Information Security Communications Plan | |
| CI1 | ISMS Performance Report | ★ |
| ISG1 | Information Security Steering Group Terms of Reference | |
| ISG2 | Information Security Group Meeting Minutes | ★ |
| Pre-Audit | Pre-Audit Checklist – Stage 1 & Stage 2 Readiness | |
| Procedures & SOPs (10) | ||
|---|---|---|
| M1 | Secure Development Guidelines | |
| M2 | Control of Documents within the ISMS | ★ |
| M3 | SOP Template (Empty) | |
| M4 | Data Transfer Guidelines | |
| M5 | Joiners, Movers & Leavers Checklist | |
| IA1 | Internal Audit Procedure | |
| IR1 | Incident Reporting SOP | |
| IR2 | Major Incident Report Template | |
| IR3 | Cyber Security Incident Response Plan | |
| CI2 | Nonconformity Process | |
| Risk Management (3) | ||
|---|---|---|
| RT1 | Risk Assessment & Treatment Methodology | ★ |
| RT2 | Risk Treatment Plan Template (Empty) | ★ |
| RT3 | Risk Appetite Statement | |
★ = a document ISO 27001:2022 explicitly requires. The rest are the supporting set a small, cloud-first business typically needs; every document is adaptable and none is padding.
The Registers
Registers of records that become your audit evidence.
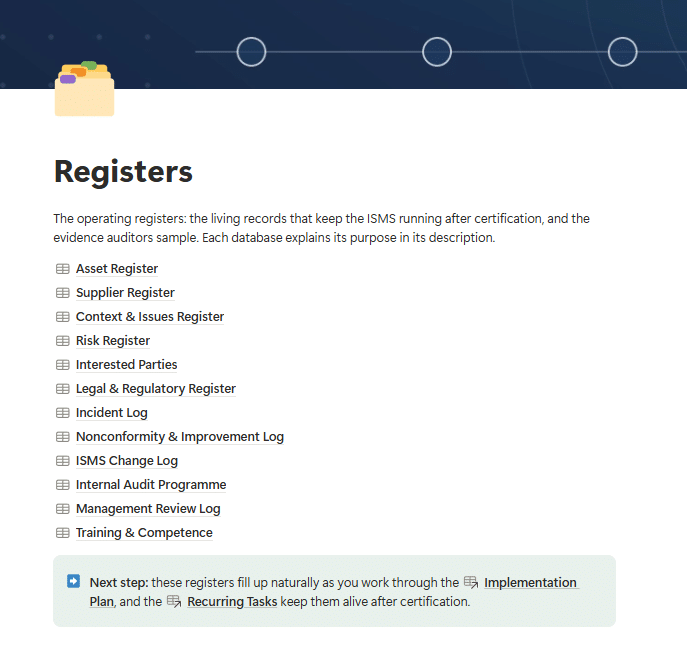
The twelve operating registers are the living records that keep the ISMS running after certification, and the evidence auditors sample. Several arrive pre-seeded with worked examples, so you start by editing a list rather than facing a blank page.
| Register | What it records | Evidences |
|---|---|---|
| Risk Register | Risks scored on a coloured five-by-five matrix, with treatment plans, residual scores and owner sign-off; worked examples included | Clauses 6.1, 8.2, 8.3 |
| Context & Issues Register | The internal and external issues that shape your ISMS, pre-seeded with the usual suspects for a small, cloud-first business | Clause 4.1 |
| Interested Parties | Who has a stake in your security – clients, regulators, staff, suppliers – and what they expect, with review dates | Clause 4.2 |
| Asset Register | Your information assets – devices, SaaS services, data stores – with owners and classification | Controls 5.9-5.13 |
| Supplier Register | Suppliers and the services they provide, their criticality, and security review dates | Controls 5.19-5.22 |
| Legal & Regulatory Register | The laws, regulations and contractual obligations that apply to you | Controls 5.31, 5.34 |
| Incident Log | Security events and incidents, their severity, response and lessons learned | Controls 5.24-5.27 |
| ISMS Change Log | Changes to the ISMS and significant organisational or technical change, with a change template and worked example | Clause 6.3, control 8.32 |
| Internal Audit Programme | The audit schedule, scope of each audit, and findings raised | Clause 9.2 |
| Management Review Log | Management reviews with the inputs and outputs the standard requires | Clause 9.3 |
| Nonconformity & Improvement Log | Nonconformities, corrective actions and improvement ideas, tracked to closure | Clause 10 |
| Training & Competence | Who has had what security training, and the competence behind each ISMS role | Clauses 7.2, 7.3 |
Each register links back to the clauses and controls it serves, so at audit you can show the evidence trail rather than hunt for it.
Tracking
A centralised dashboard to help you track progress.
Video guides
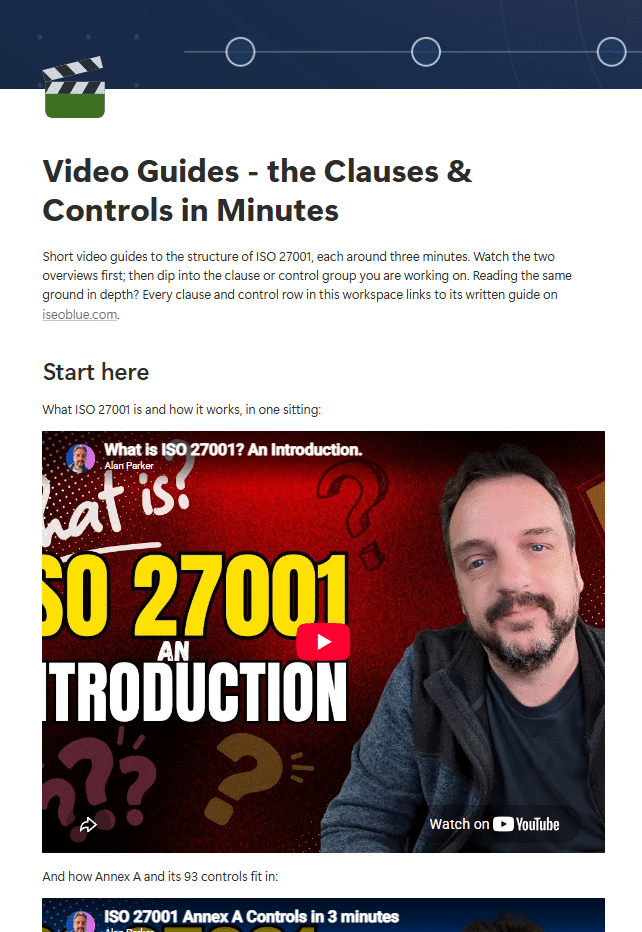
Every clause and control group explained in around three minutes.
Price Comparison Against Other Online Solutions
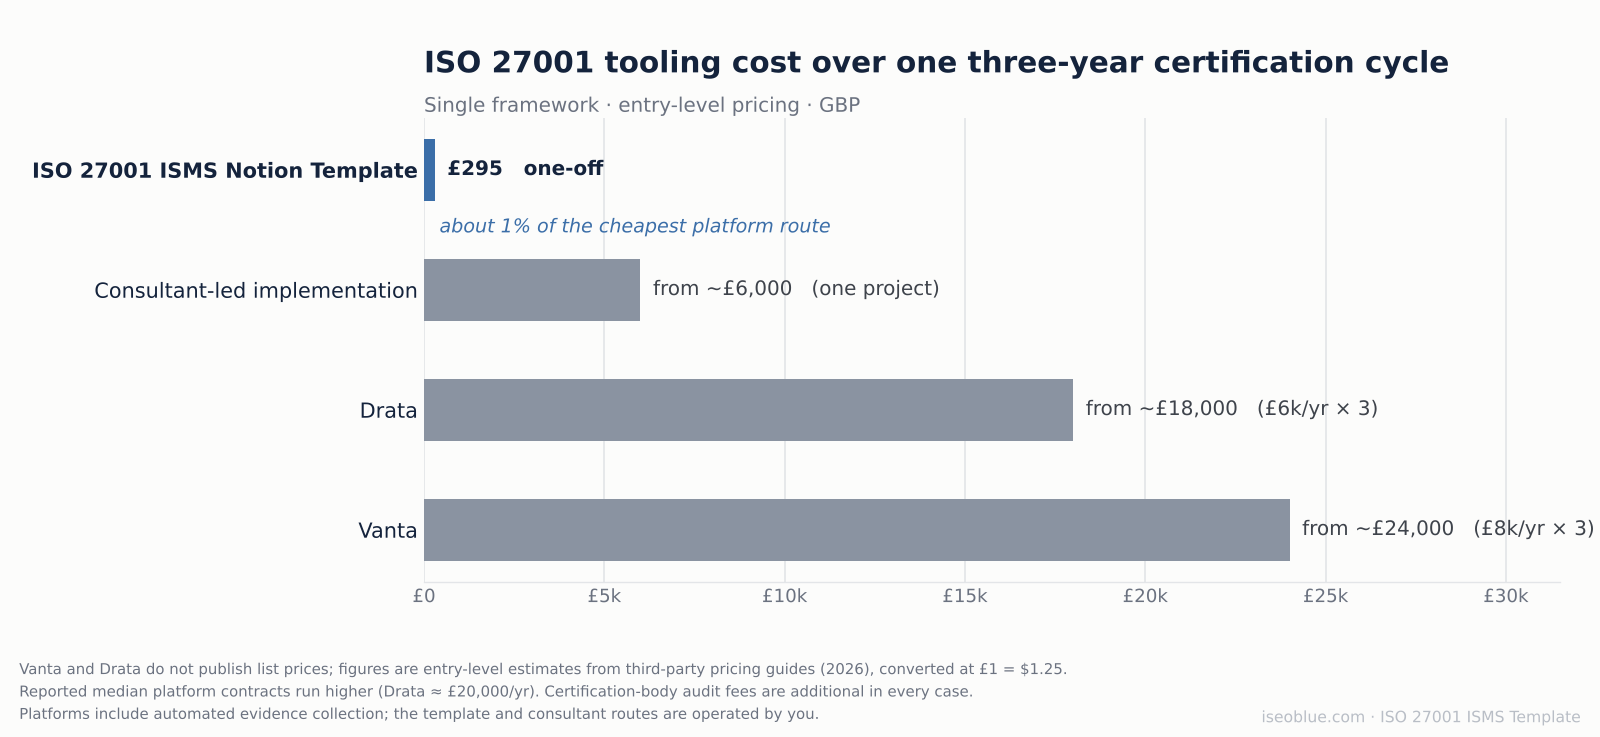
If you are a small, remote team running on cloud and SaaS and chasing certification to win contracts, this was built for you.
It is deliberately not an enterprise toolkit of four hundred documents.
Minimal Viable Compliance means what certification actually requires, and no over-engineered solutions. For the full comparison of platforms, toolkits and consultants, with sourced prices, read Vanta alternatives for ISO 27001 or, if Drata is the one quoting you, Drata alternatives for ISO 27001.
How it works
- Buy ISO 27001 in a Box. Your receipt arrives with your access link.
- Open the link and click Duplicate. The whole system copies into your own Notion workspace; a free Notion account is fine.
- Open Getting Started and follow the plan.
Who built it
I am Alan Parker, a certified ISO/IEC 27001:2022 Lead Auditor with around 30 years in IT governance and security.
I implement and audit ISO 27001 for small businesses for a living; ISO 27001 in a Box is the approach I use for those engagements.

Questions
Do we need a paid Notion plan?
No. ISO 27001 in a Box duplicates into a free Notion account. However, you may decide you require the business or enterprise plans based on your team’s needs. Pricing for Notion is here.
Will this get us certified?
No toolkit can promise that; certification depends on you operating the system. What this removes is the guesswork: what to write, what evidence to keep, and what order to do it in.
How many people can use it?
Everyone in your organisation. The licence covers one organisation; consultants wanting to use it with clients should ask about a consultant licence.
What other costs might there be to get ISO 27001?
1) I’d recommend you purchase the standard itself (so many try to do it without it, which I can never recommend). Get the ISO 27001 standard here.
2) If you can’t find the resources internally to conduct an internal audit (which must prove impartiality and competancy), then you may need to bring in an external auditor to help you. My internal auditor service and costs are here.
3) Your auditor costs for the certification itself. I’ve explored those in my ISO 27001 Auditing Costs Guide here.
What if we get stuck?
Email alan.parker@iseoblue.com and I will point you in the right direction. For structured help, I also offer internal audits and coaching.
One-off payment, VAT invoice included.
Single-organisation licence; full terms at iseoblue.com/toolkit-terms.